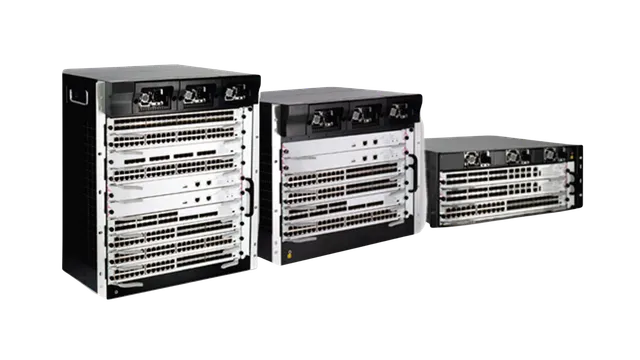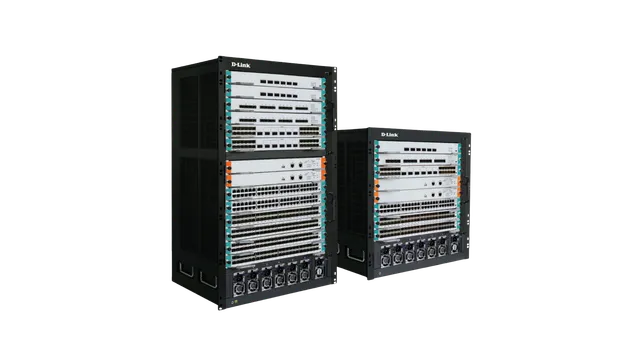
DGS-9600E Series is a new generation high-performance core switch oriented for high performance computing, data center and high-end campus networks. DGS-9600E Series adopts advanced hardware architecture design. DGS-9600E supports a maximum of 576 10G ports, 72 40G ports, and 72 100G ports. DGS-9600E Series provides high-performance L2/L3/L4 wire speed switching capacity by integrating services such as IPv6, network security, flow analysis, virtualization. With highly reliable techniques including continuous forwarding, graceful restarting and loop network protection, the work efficiency of DGS-9600E Series and its maximum running time are guaranteed. DGS-9600E Series supports Green architecture. DGS-9600E Series has two models: DGS-9608E and DGS-9614E.
DGS-9608E
DGS-9600E Series Chassis Switches
- DGS-9600E is a high-performance cloud computing, data centers, and high-end campus networks switch series. The DGS-9600E series features an advanced hardware architecture, delivering the industry's highest switching performance and a rich array of data center business features.
- DGS-9600E series supports up to 576 10G ports, 72 40G ports, and 72 100G ports.
Overview
Advanced Hardware Architecture and Industry-Leading Processing Capacity
Designed for 100G Platforms: Features an industry-leading distributed multi-stage switching matrix architecture, equipped with high-performance ASIC switching chips and multi-core processors, meeting the requirements for high performance, high capacity, high density, and scalability of carrier-grade core devices. Supports High-Density 10G line cards: Enables full line-rate, non-blocking Layer 3 switching across cards. Port Capacity: Supports up to 576 10G ports, 72 40G ports, and 72 100G ports.
Rich Business Features
Complete Layer 2 and Layer 3 multicast routing protocols meet the access needs of IPTV, multi-terminal HD video surveillance, and HD video conferencing. Comprehensive Layer 3 routing protocols with large routing table capacity meet various network interconnection needs, enabling the construction of ultra-large campus networks, enterprise networks, and industry-specific private networks. Enhanced service security mechanism: Supports plaintext or MD5 authentication for related routing protocols, supports uRPF reverse path forwarding technology for effective illegal service control; hardware-level deep packet inspection and filtering technology supports deep inspection of control and data packets, effectively isolating illegal data packets, and improving network system security.
Innovative VSS Technique
Supports Innovative Virtual Switch System: Enables virtualization of multiple physical devices into a single logical device. Compared to standalone physical devices, the virtual system offers unparalleled advantages in performance, reliability, flexibility, and management. Performance Boost: The virtualization system fully utilizes every link between physical devices, eliminating the link blocking caused by the Spanning Tree Protocol in traditional network models. This maximizes the use of existing links, doubling performance and protecting original link investments to the greatest extent. High Reliability: Based on advanced distributed processing technology, the system leverages efficient cross-device link aggregation to achieve three-plane separation: logical control plane, service control plane, and service data plane. This ensures uninterrupted Layer 3 routing and forwarding, avoiding service interruptions caused by single-point failures and significantly enhancing system reliability. Ease of Management: The entire virtual system is managed through a single unified IP, making the underlying physical devices transparent to the user. This simplifies the management of network devices and topologies, greatly improving network operational efficiency and effectively reducing operational and maintenance costs.
Carrier-Grade Reliability
HPS (Hitless Protection System): Ensures redundancy for key components (system control unit, power system, fan system) and hot-swappable system modules, allowing seamless switching during failures without manual intervention. Supports STP/RSTP/MSTP protocols, VRRP protocol, ring network protection, dual uplink master-slave link protection, and LACP link aggregation for efficient redundancy protection mechanisms. Supports ISSU (In-Service Software Upgrade) for nonstop system upgrades, and GR (Graceful Restart) for OSPF/BGP routing protocols, ensuring uninterrupted user data forwarding during system upgrades and master control switching. High-precision BFD bi-directional link detection mechanism provides millisecond-level fault detection and service recovery, greatly improving network system reliability. High-reliability design meets telecom-grade service recovery time requirements of 50ms, achieving carrier-grade core equipment's 99.999% high reliability.
Comprehensive IPv6 Solutions
Fully supports IPv6 protocol suite, including IPv6 neighbor discovery, ICMPv6, Path MTU discovery, DHCPv6, and other IPv6 features. Supports IPv6-based Ping, Traceroute, Telnet, SSH, ACL, and other management and service control needs for pure IPv6 network equipment. Supports MLD, MLD Snooping, IPv6 static routing, RIPng, OSPFv3, BGP4+, and other IPv6 Layer 3 routing protocols, providing comprehensive IPv6 Layer 2 and Layer 3 solutions.
Comprehensive Security Mechanisms
Device-level security protection: Advanced hardware architecture design provides hierarchical scheduling and protection for packets, supports DoS, TCP SYN Flood, UDP Flood, broadcast storm, large traffic, and other attack prevention; supports 6KV port lightning protection; supports command line hierarchical protection with different management permissions for different level users. Comprehensive security authentication mechanism: Supports IEEE 802.1x, Radius, Tacacs+, providing a complete security authentication mechanism for users.
Innovative Green Environmental Design
Intelligent power management system: Adopts an advanced power system architecture design for efficient power conversion, unique power monitoring, soft start, sequential power-on, and other functions, real-time monitoring of the whole machine operation status, intelligent adjustment, deep energy saving. Intelligent fan management system: Intelligent fan design supports automatic speed adjustment and independent partition control, effectively reducing speed and noise and extending fan life. Supports Energy Efficient Ethernet function, compliant with international standard IEEE 802.3az, effectively reducing energy consumption.
DGS-9608E
Specifications
| Switching Capacity | 32Tbps |
|---|---|
| Forwarding Rate | 5357Mpps |
| Slot Number | 8 |
| Line Card Slot | 6 |
| Power Supply | AC:100V-240V |
| Power Slots | 7 |
| Overall Weight (Empty) | 30.2Kg |
| Dimensions | 485.7 x 482.6 x 370mm |
| MAC Switching Capacity | Static configuration and dynamically learning of MAC address Check and clear MAC address Configuring of MAC address aging time Limit on MAC address learning number MAC address filtering function Black-hole MAC items IEEE 802.1AE MacSec Security Control |
| VLAN | 4K VLAN entries GVRP 1:1 and N:1 VLAN Mapping Basic QinQ and selective QinQ Private VLAN |
| STP | 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP) BPDU protection, root protection and ring protection |
| Multicast | IGMP v1/v2/v3 IGMP Snooping IGMP Fast Leave Multicast group policy and multicast number limit Multicast traffic cross VLAN duplication PIM-SM and PIM-DM |
| Management and Maintenance | Console, Telnet and SSH SNMP v1/v2/v3 Upload and download of TFTP files Remote Network Monitoring (RMON) Statistics analysis of sFLOW |
| IPv4 | Static routing, RIP v1/v2, OSPF and BGP Policy routing Load balance through equal-cost routing Graceful Restart of OSPF and BGP BFD for OSPF and BGP |
| IPv6 | ICMPv6, DHCPv6, ACLv6, IPv6 Telnet IPv6 Neighbor Discovery Path MTU Discovery MLD and MLD Snooping IPv6 static routing, RIPng, OSPFv3 and BGP4+ Manual tunnel, ISATAP tunnel and 6-to-4 tunnel |
| QoS | Traffic classification of each field of L2/L3/L4 protocol headers CAR traffic control 802.1P/DSCP priority remark Multiple queuing algorithms such as SP, WRR or SP+WRR Tail-Drop, WRED Traffic supervision and traffic shaping Ingress and Egress ACL, and matching L2, L3, L4 and IP quintuples for copying, forwarding and discarding Hash algorithms and load balancing |
| Environment | Operating temperature/humidity: 0°C-40°C; 10%-90% non-condensing Storage temperature/humidity: -20°C-70°C; 5%-95% non-condensing |
| Security Features | Identification and filtering of L2/L3/L4 based ACL Defend against DOS or TCP attacks Suppression of broadcast, multicast and unknown unicast packet Port isolation Port security, IP+MAC+port binding DHCP Snooping, DHCP Option 82 IEEE 802.1x authentication Radius and Tacacs+ authentication uRPF Command line authority control based on user levels |
| Reliability | Dual Master Control Redundancy Power M+N backup Master control, service card hot swap and service automatic recovery Static/LACP link aggregation and cross service card link aggregation Ring network protection including EAPS VRRP GR for OSPF and BGP BFD for OSPF and BGP |
| Energy saving | IEEE 802.3az Energy Efficient Ethernet |
| Value-added services | IEEE 802.3az green Efficient Ethernet |
Actual performances may vary due to settings, cabling, temperature, network configuration, interface, device compatibility, environmental and on-site conditions, and other similar factors. References to power capability, signal or processing speed, signal range or distance, data encryption, storage capacity, display properties, or other performance metrics are based on optimal conditions derived from industry standards and provided for informational purposes only. Specifications may be subject to change without prior notice.